After learning about the capabilities offered by the Early Warning System (SAT), an organization’s decision may hinge on a practical question: what does actually incorporating it into their infrastructure entail?
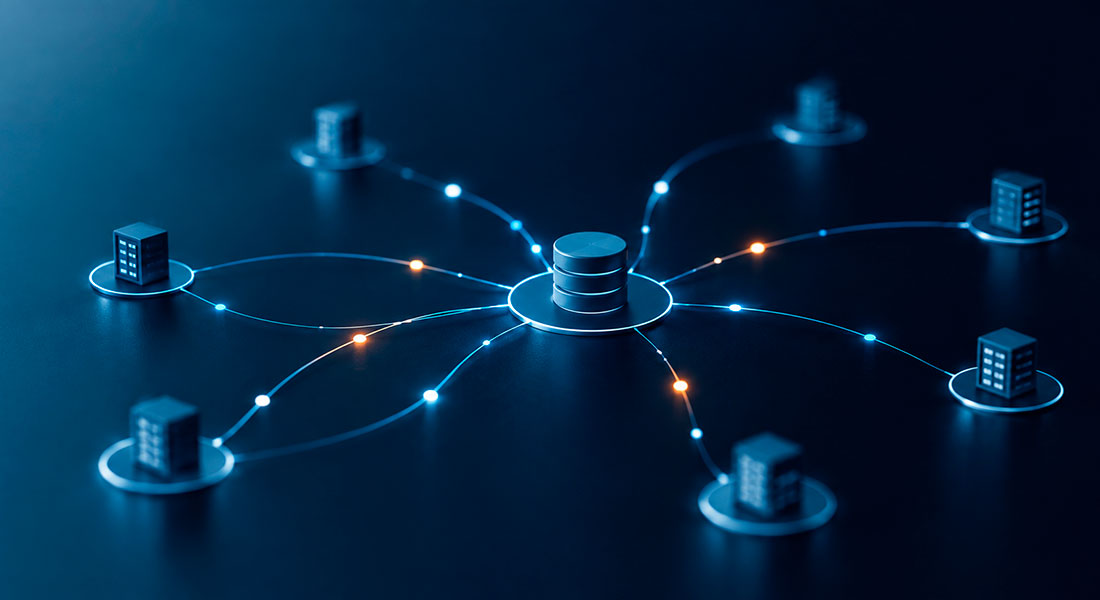
The answer depends on the specific service (SAT-INET or SAT-ICS) and the environment being monitored, but both operate on a similar principle. Deploying a probe allows for the analysis of a traffic copy and the generation of events, which are then sent to the CCN-CERT central system for analysis.
This means that integrating SAT does not require replacing existing security solutions or altering standard network operations. The system complements existing capabilities and provides an additional source of information for security teams.
A probe that monitors traffic without interfering with it
In SAT-INET, the probe analyzes a copy of the organization's Internet traffic. Various detection mechanisms and rules are applied to this traffic to identify potentially malicious activity. Relevant events are securely transmitted to the CCN-CERT central system, where analysis and correlation take place.
For SAT-ICS, the approach is adapted to industrial networks and SCADA systems. Monitoring is likewise passive: the probe receives a copy of the traffic, enabling the analysis of communications without interfering with the processes being supervised.
Once the service is deployed, the organization has access to the SAT portal. Through this interface, authorized security personnel can view events related to their organization.
In SAT-INET, the portal provides access to detected security events in real time and allows for the generation of reports. SAT-ICS also incorporates capabilities related to asset and communication visualization, statistics, and information regarding identified anomalies.
The SAT thus integrates into the security team's workflow as an additional source of information on what is occurring within the infrastructure.
What should be clear before joining
Although a good part of the technical management of the system corresponds to the CCN-CERT, having the SAT does not eliminate the need to have capacity within the organization to take advantage of the information it provides.
An alert gains value when there is a team capable of analyzing what it means for its environment, contrasting it with other sources and acting when necessary.
Therefore, before addressing the incorporation it may be useful to review some questions:
- What networks or environments do we want to monitor?
- Do we need surveillance of Internet traffic, industrial or cyber-physical environments, or both?
- Who will be responsible for consulting and using the information provided by the SAT?
- How will your alerts be incorporated into regular incident analysis and management procedures?
- What internal sources can we consult to expand a detection received through the system?
- Is there a clear procedure for escalating an alert when it is confirmed that it requires action?
These are simple questions, but they help prevent incorporation from being considered solely as the deployment of a new technology.
The CCN-CERT assumes the management, updating and maintenance of the central components of the system and maintains the detection capabilities that support the service. For the organization, the real work begins when that information reaches its security teams and is incorporated into its operations.
The three previous articles in this series have shown different ways in which SAT can expand this operation: providing new detection capabilities, relating information from different organizations and improving visibility over assets and communications in industrial environments.
Incorporation into the system allows these capabilities to be brought together within a common service. The objective is not to accumulate one more tool, but to have information that helps the organization to identify a threat sooner and make better decisions when it appears.
Therefore, evaluating membership in the SAT requires looking beyond the technical deployment. The relevant question is how the information it provides can be integrated into the processes that the agency already uses to detect, analyze and respond to a possible incident.